Nevertheless, crucial change concerning constrained devices is the introduction of a new content kind referred to as ACK. A DTLSv1.3 endpoint can use acknowledgment messages when it detects disruptions in the course of the reception of a DTLS flight. The draft proposes to arm a timer for 1/4 of the duration of the present retransmission timer timeout after a disruption is detected. When the timer expires, the endpoint generates an acknowledgment for the elements of the flight that have been well-received and appropriately processed by together with a listing of the record numbers in the acknowledgment message. Upon reception of an acknowledgment the sender disables the retransmission timer and retransmits solely the report fragments that were misplaced. The results obtained in the previous part show that the retransmission behavior of DTLS is ill-suited for constrained networks.
Requirement: Hardware Validation Failure Service Request
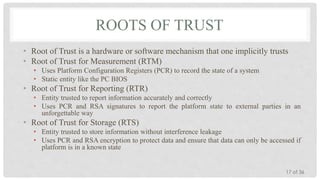
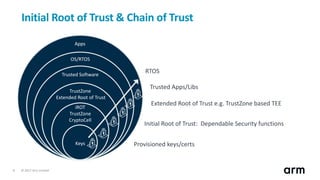
The PSA Root of Trust (PSA-RoT) is a supply of confidentiality (for example, crypto keys) and integrity. The PSA-RoT defines what it takes for a hardware or software program system to be trusted. Mbed TLS is a C library that implements cryptographic primitives, X.509 certificates manipulation, and the SSL/TLS and DTLS protocols.
Signatures are valid provided that each the classical and quantum elements verify successfully, ensuring resilience even when one algorithm is compromised. In 2013, the IETF began engaged on a new model of the TLS protocol, referred to as TLSv1.3 30. The newest iteration of the TLS protocol contains some vital enhancements which might be also attention-grabbing for low-power devices. Not only does the new specification improve the safety of the protocol but it additionally reduces the latency of the handshake phase. While TLSv1.2 takes two full RTTs till application information may be exchanged, TLSv1.three by default only requires one RTT.
We discover, with Nagle lively, a rise between ±10% and ±2% within the variety of transmitted bytes for an MTU of 356 B and 864 B, respectively. Similarly, we see an increase between ±10% and ±15% when Nagle is not active. Evaluating the handshake length, we measure an increase between ±15% and ±10% with Nagle energetic and ±11% with Nagle inactive.
System Safety Configuration Information For Cisco 8000 Series Routers, Ios Xr Releases
The integration shall additionally adjust to NIST SP A 16—requirements for random quantity era. An example QRNG methodology combining entropy from two sources, to be used in ML-KEM, is illustrated in the Figure 1. This part takes a better take a look at the O-RAN structure, specializing in its modular design and security features which are already in place. We then introduce the fundamentals of post-quantum cryptography and discuss how present safety protocols have to evolve to stay protected against future quantum threats. Attestations allow exterior verifiers to verify the integrity of the software program working on the host.
How Chip Guard Hardware Integrity Checks Work
The benefit of uneven cryptography is that the process of sharing encryption keys does not need to be secure, however the mathematical relationship between public and private keys means that much bigger key sizes are required. The public key is mathematically related to the personal key, but given enough key length, it’s computationally impractical to derive the non-public key from the general public key. This allows the public key of the recipient to be used by the sender to encrypt the data they want to ship to them, but that information can only be decrypted with the personal key of the recipient.
The embedded attack floor, strolling from hardware as a lot as community, has six layers price distinguishing. Each layer has its personal vulnerability lessons and its own defensive disciplines, and an entire embedded security program addresses all six rather than treating the system as a monolith. IEC makes use of https://womenbabe.com/cryptocurrency-trading-with-the-nexaveropro-platform.html the concept of Security Requirements as nicely as Security Levels to classify the safety features and safety functionality for industrial control techniques and gadgets. Gadgets fulfilling those Safety Necessities and Security Ranges might achieve a security certificates if reviewed by an accredited auditor. In TLS (e.g., TLS 1.3 39), these bigger certificate payloads are transmitted over TCP, utilizing segmentation and TLS record-layer fragmentation 40. However, the effectivity of this course of is influenced by the initial TCP congestion window and the conduct of the selected congestion management algorithm.
- Prior analysis, corresponding to 20, has addressed post-quantum safety enhancements for specific protocols like IPsec and MACsec in RAN contexts.
- The RTT can significantly increase when constrained devices are computing the cryptographic capabilities, see Determine 8a.
- Full TLS stacks, fashionable cryptographic libraries, and the operating system providers that summary security on richer platforms are sometimes unavailable.
- Upon reception of an acknowledgment the sender disables the retransmission timer and retransmits only the document fragments that have been lost.
The pragmatic pattern is to use ASVS because the baseline verification commonplace and add embedded-specific verification necessities on top, somewhat than substituting an embedded-specific normal totally. Modern embedded silicon more and more includes a safe factor — a hardware-isolated key store that holds cryptographic keys in a region the appliance processor can not directly read. The application asks the secure element to signal or decrypt; the secure element performs the operation with out exposing the necessary thing materials. Examples embody ARM TrustZone’s safe world, NXP’s EdgeLock SE050, Microchip’s CryptoAuthentication chips, and Espressif’s safe storage on ESP32. The sample is the gold commonplace for embedded secret storage — even an attacker with full physical access can not extract the keys with out specialised hardware attacks properly beyond commodity functionality.
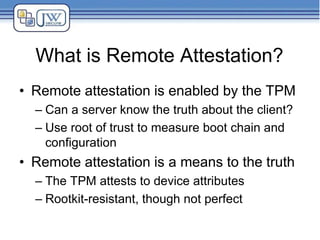
If counterfeit chips are detected, secure boot is halted, preventing compromised units from entering the network. Hardware-anchored root of trust is enabled by default on Cisco 8000 Series Routers. Verifying the hardware belief standing ensures device integrity and compliance. In Contrast with Profile Small, Profile Medium goals to securely connect units toCloud providers with asymmetric cipher support.Profile Medium target gadgets need extra assets for more cipher algorithmsand higher isolation levels. Increasingly highly effective silicon is on the nerve center of IoT gadgets, enabling them to gather, process, and transmit knowledge.
Eu Cyber Resilience Act: Secure Growth Developer Information
In the second phase, the friends switch cryptographic parameters to derive the shared master secret. Relying on the authentication methodology and the selected cipher suite, for instance, after they use ECDHE_ECDSA as a key exchange methodology, the server sends a ServerCertificate message. The first certificates within the chain is the server’s certificates, the last one is a self-signed certificates, doubtlessly from a root Certificates Authority (CA), and represents the trust anchor. TLS and DTLS also help Pre-shared key (PSK) and raw public key (RPK) authentication.